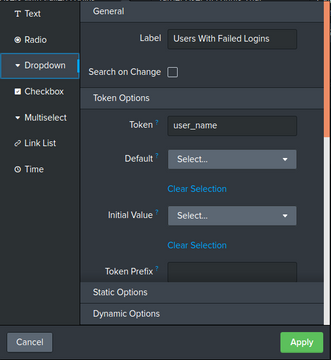
Solved: How to set a splunk token in a search query - Splunk Community

Kitchens4,222 ideas

Bathrooms2,442 ideas

Kids Rooms1,868 ideas

Bedrooms1,657 ideas

Powder Rooms1,638 ideas

Family Rooms1,414 ideas

Dining Rooms1,403 ideas

Laundry1,361 ideas

Basements1,338 ideas

Entries1,286 ideas

Home Bars1,168 ideas

Hallways1,131 ideas

Home Offices1,098 ideas

Living Rooms1,038 ideas

Nurseries923 ideas

Closets & Storage922 ideas

Sunrooms851 ideas

Decks792 ideas
“Splunk Token”
0 in catalog · +120 from web
More from the web

Splunk Kafka Token – Configure Splunk Connect for Kafka – ICXLO

Splunk Web Framework : Token management in Splunk JS - YouTube
Solved: How to set a splunk token in a search query - Splunk Community
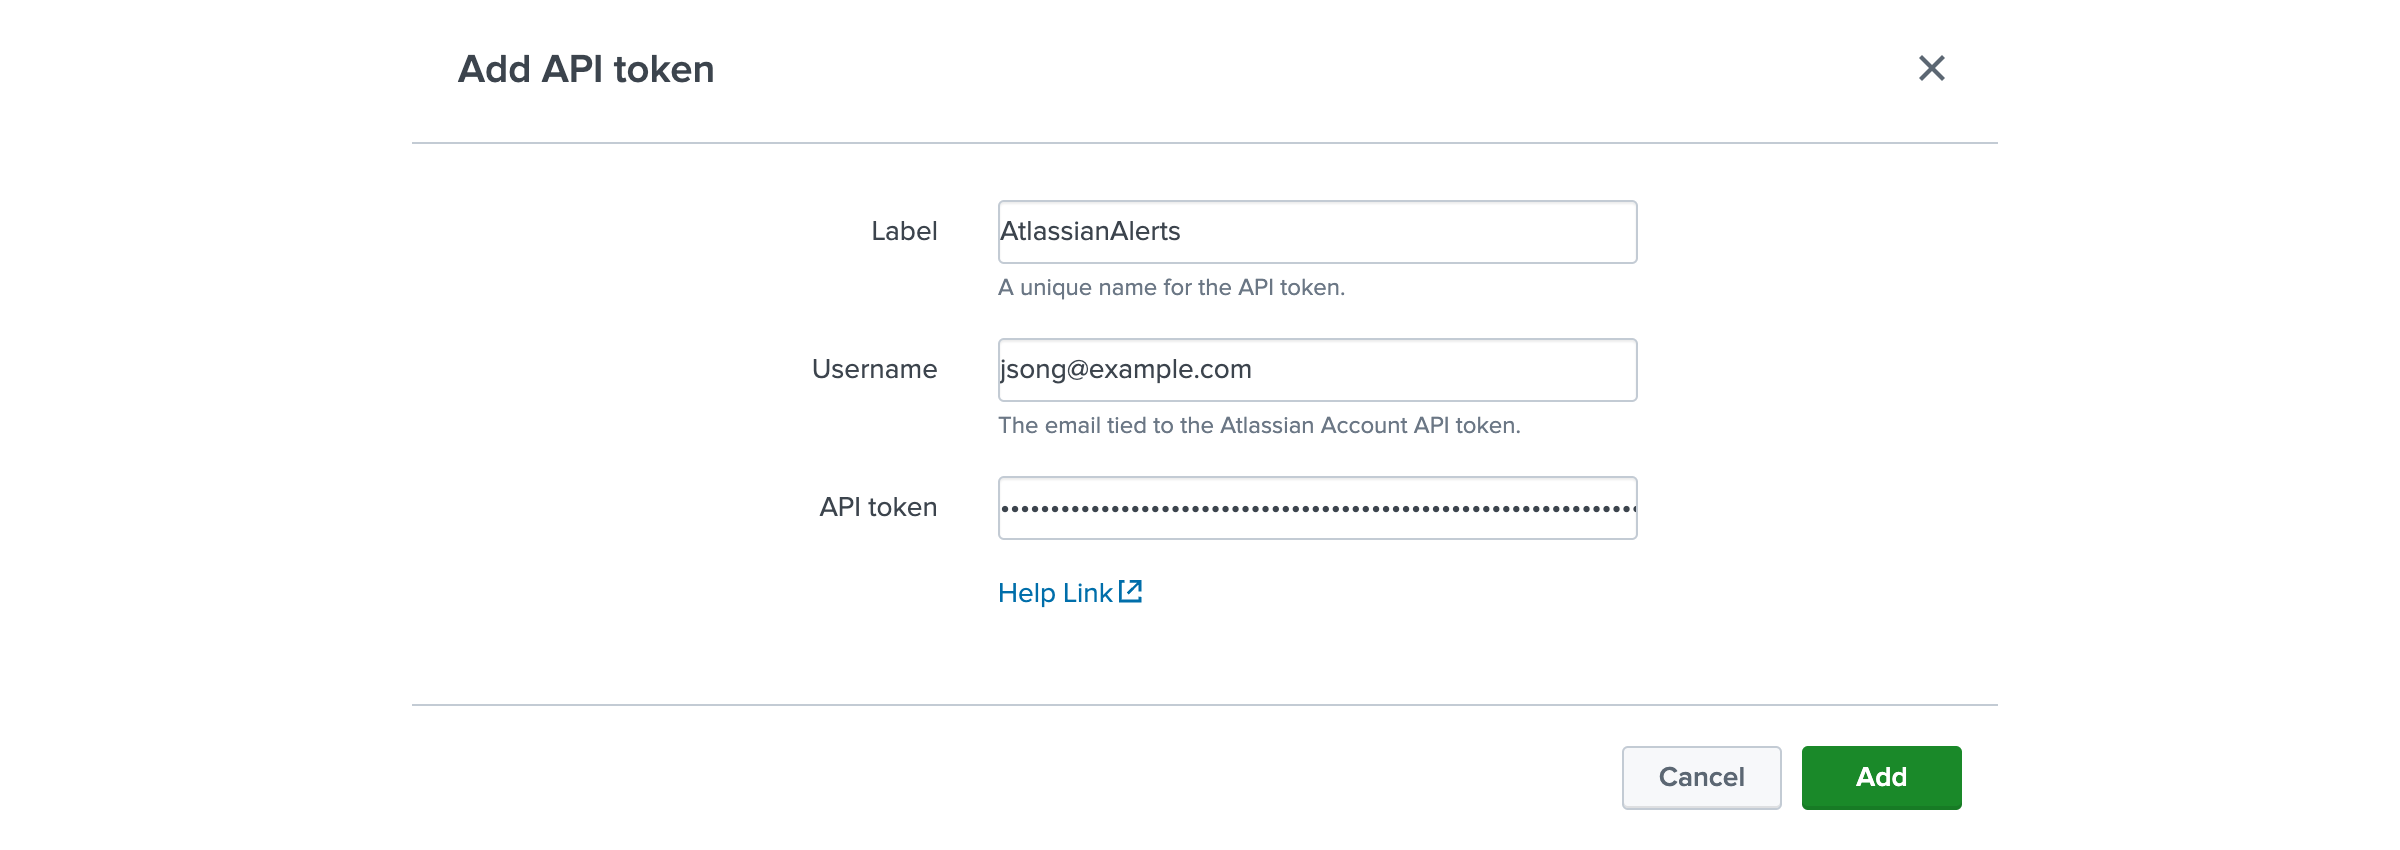
Splunk Add‑On for Jira Cloud – API Token Validation Error | Splunk

Pass a drilldown token from one Splunk dashboard to another dashboard ...
Default Token - Dashboard Studio - Splunk Community

Configure HTTP Event Collector in Splunk Web - Kinney Group

Splunk

Configuring the Splunk System

Splunk O11y Deployment

Splunk Integrations for Gravwell

Integration with Splunk | NetScaler® Console service

Splunk Integration | Embrace Documentation
Use the Splunk Connector

Splunk

Splunk Configuration

Configuring Splunk HEC

Splunk TA Overview - IP Fabric Documentation Portal

Integrate SSH Jump server with splunk for SIEM
Use the Splunk Connector

Splunk - BlinkOps Documentation

Dashboard Studio: It's the Little Things | Splunk

Splunk Using Tokens to Perform Completely Different Searches - YouTube

SIEM Configuration Guide for Splunk Enterprise and Cloud Platform | Zscaler

Aggregating Ansible Tower logs to Splunk
Use the Splunk Connector

Splunk Enterprise & Cloud

APISIX Splunk Integration: Send Logs via HEC | Apache APISIX
Set up a token-based auth connection to Splunk – Celigo Help Center

Splunk integration – Help Center

Splunk Dashboard tokenの細かい話(処理タイミング編)

Splunk

Splunk | Knowledge Base

Sending Logs to Splunk Enterprise and Splunk Cloud

Getting data from your REST APIs into Splunk | Splunk

Getting Data into Splunk | PPTX

Splunk Integration

Dashboard Studio: How to Configure Show/Hide and Token Eval in ...
Use the Splunk Connector

Dashboard Studio: It's the Little Things | Splunk

CREATING A SPLUNK CLOUD CONNECTION | ThingParkX

Getting Okta data into Splunk - Somerford Associates

Getting Okta data into the Splunk platform - Splunk Lantern

Splunk | GitGuardian documentation
Security in Obscurity - Different ways to use a $token$ in Splunk

Splunk Observability - BlinkOps Documentation

What is the Splunk REST API?

Mule and Splunk Integration
Integrate Opsgenie with Splunk | Opsgenie | Atlassian Support

How To Set Up Splunk Real User Monitoring | DebugBear

Splunk .conf 2019: Fields, Indexed Tokens and You - iDelta
Security in Obscurity - Different ways to use a $token$ in Splunk

Splunk Integration | Embrace Documentation
Splunk Dashboarding - Ontitansshoulder

Splunk Remote Deployments (splunkremotesearch) - TrackMe documentation

Splunk configuration file for the cloud | PDF

Monitoring resources in an AWS Control Tower environment using Splunk ...

Tokens Analysis dashboard on Splunk - YouTube
Security in Obscurity - Different ways to use a $token$ in Splunk
Integrating Splunk with BetterCloud

Splunk

Splunk | GitGuardian documentation
Use the Splunk Connector

How to find anomalies in the sea of Splunk Zeek data | Elastic Blog

Integrate with Splunk

Splunk Remote Deployments (splunkremotesearch) - TrackMe documentation

How To Set Up Splunk Real User Monitoring | DebugBear

Deception and Splunk Deployment Guide | Zscaler

Splunk Remote Deployments (splunkremotesearch) - TrackMe documentation

Splunk integration | Bugsee

Splunk Developer Program

Splunk | FusionAuth Docs

Integrating Ansible Automation Controller with Splunk | techbeatly
Security in Obscurity - Different ways to use a $token$ in Splunk

Splunk - BlinkOps Documentation

Dashboard Studio: New Features Highlighted At .conf21 | Splunk

How To Set Up Splunk Real User Monitoring | DebugBear
Splunk integration – Help Center

Mule and Splunk Integration

Splunk y Microsoft Security Copilot | Microsoft Learn
Automation Suite - Configuração do Splunk

Ingesting events using Splunk Cloud for administrators
Send alerts to Splunk | Atlassian Support

Logging to Splunk | Nametag Developer Documentation

Splunk Remote Deployments (splunkremotesearch) - TrackMe documentation
Use the Splunk Connector

Dashboard Studio: How to Configure Show/Hide and Token Eval in ...

How to Configure Fluent Bit and Splunk in Tanzu Kubernetes Grid ...

Dashboard Studio: How to Configure Show/Hide and Token Eval in ...
Solved: how to call the functions using token? - Splunk Community

Configuring Splunk HEC

Splunk Integration | Embrace Documentation

Dashboards Beta v0.8: Examples Hub | Splunk

Splunk Dashboard tokenの細かい話(時刻処理の話)

How to use tokens from 2 time range inputs in single Splunk dashboard ...

CREATING A SPLUNK CLOUD CONNECTION | ThingParkX

Splunk Setup

Setting up Splunk for OpenTelemetry Export

Splunk EnterpriseとSplunk SOARの環境を構築する
Security in Obscurity - Different ways to use a $token$ in Splunk

Preparation - Splunk OpenTelemetry Workshop

Splunk cloud integration guide
Use the Splunk Connector

Splunk (SAPM) (Deprecated) - Odigos

Ingesting audit events to Splunk - Documentation Center

Docker loves Splunk | 64° Adventures
Access Tokens Page - New & Improved - Splunk Community

Splunk Integration | Embrace Documentation

Log Platform Integration Practices EdgeOne Real-Time Log Push to Splunk ...

Splunk (SAPM) (Deprecated) - Odigos

The Migration Tool — Gravwell v5.9.0 documentation

See Intro to HEC Tokens in Splunk, creating, onboarding and ...

Splunk's api how we built it | PDF

Creating a New Input

Business Impact

See Intro to HEC Tokens in Splunk, creating, onboarding and ...