Solved: Set x-axis over multiple topic at line graph - Splunk Community

Kitchens4,222 ideas

Bathrooms2,442 ideas

Kids Rooms1,868 ideas

Bedrooms1,657 ideas

Powder Rooms1,638 ideas

Family Rooms1,414 ideas

Dining Rooms1,403 ideas

Laundry1,361 ideas

Basements1,338 ideas

Entries1,286 ideas

Home Bars1,168 ideas

Hallways1,131 ideas

Home Offices1,098 ideas

Living Rooms1,038 ideas

Nurseries923 ideas

Closets & Storage922 ideas

Sunrooms851 ideas

Decks792 ideas
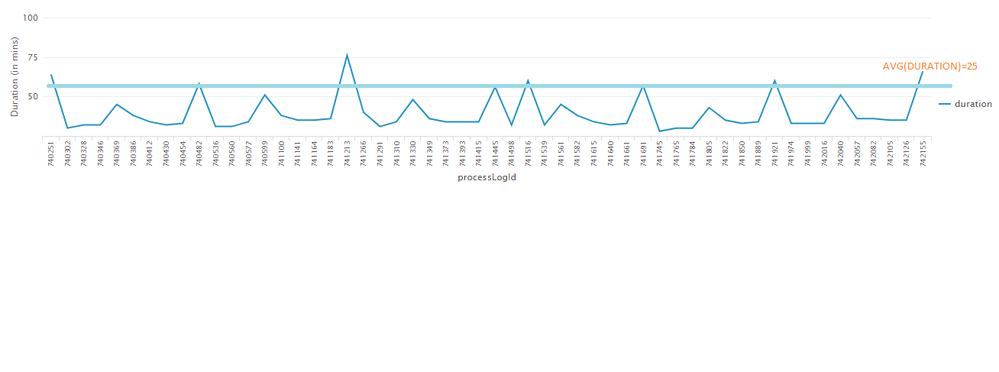
“Over Treshold Splunk Graph”
0 in catalog · +120 from web
More from the web

Solved: How do I plot a static value over time that is der... - Splunk ...

Solved: One Chart - one search and data plot over 2 separa... - Splunk ...

Splunk Chart Over , Commandes de recherche > stats, chart et timechart ...

Solved: How to change dashboard panel from line graph to p... - Splunk ...
mouse over in Radar chart - Splunk Community
How to modify the color coding of a forecast graph - Splunk Community

Comparing Values Over Specific Times With Splunk Dashboards
Solved: Splunk Graph using 4 Fields combination - Splunk Community
Solved: Re: Add a value "0" and make it visible on a graph - Splunk ...
How to modify the color coding of a forecast graph - Splunk Community

How to Customise Detectors for Even Better Alerting | Splunk

Quick Guide to Outlier Detection in Splunk - Discovered Intelligence

A guide to the Power of Splunk Visualizations - Kinney Group

Quick Guide to Outlier Detection in Splunk - Discovered Intelligence

Quick Guide to Outlier Detection in Splunk - Discovered Intelligence
GitHub - a5hk/threshold_viz: Splunk visualization

Quick Guide to Outlier Detection in Splunk - Discovered Intelligence
Detector Best Practices: Static Thresholds - Splunk Community

Maintaining Thresholds: Advanced Splunk Observability Detectors | Splunk
Splunk AI in ITSI cannot find correct thresholds o... - Splunk Community
Custom visualizations in the Splunk Machine Learning Toolkit - Splunk ...

Chasing a Hidden Gem: Graph Analytics with Splunk’s Machine Learning ...

Creating Charts - Splunk Observability Workshops

Using DensityFunction for Outlier Detection in Splunk

Overview of the New Charting Enhancements in Splunk 7.0 | Function1
Detector Best Practices: Static Thresholds - Splunk Community

Splunk Stacked Bar Chart

Find the Sweet Spot of Splunk Enterprise Upgrades | Splunk
Types Of Charts In Splunk at Mitchell Trigg blog

How to format splunk graphs to show multiple lines (one line for each ...

Splunk 叠加图表详解与使用示例 | Splunk 教程
How we can create a multi line chart to display th... - Splunk Community

Splunkサーチコマンド > stats、chart、timechart | Splunk

Splunk Chart Command Options | Splunk Chart Examples – AWCV
Types Of Charts In Splunk at Mitchell Trigg blog

Splunk Stacked Bar Chart

Types Of Charts In Splunk at Mitchell Trigg blog

Dashboard Design: Visualization Choices and Configurations | Splunk

A guide to the Power of Splunk Visualizations - Kinney Group

Splunkサーチコマンド > stats、chart、timechart | Splunk

Visualising Network Patterns with Splunk and Graphistry | Splunk

Flatten the SPL Learning Curve: Introducing Splunk AI Assistant for SPL ...

Machine Learning Toolkit Overview in Splunk Enterprise Security ...

A guide to the Power of Splunk Visualizations - Kinney Group

Ensuring Success with Splunk ITSI - Part 1: Thresholding Basics | Splunk
Missing data observed on Splunk Observability Cloud dashboard charts ...

Supercharge Cybersecurity Investigations with Splunk and Graphistry: A ...

A guide to the Power of Splunk Visualizations - Kinney Group

Trellis Display of two values? - Splunk Community

Solved: Column chart with Multiple chart overlay series ? - Splunk ...
Solved: Can i create trellis with overlays, when the overl... - Splunk ...

Splunk visualization made easy | Grafana Labs

Using the InfoSec App for Splunk - InfoSec App for Splunk Documentation
Chart controls | Splunk Enterprise (last updated 2025-07-04T02:35:19.666Z)

splunk timechart 複数 – splunk chart count – RMEC

Performance Insights for Splunk | Splunkbase

How can I overlay multiple fields in Dashboard Stu... - Splunk Community

How to Customise Detectors for Even Better Alerting | Splunk

Search commands > stats, chart, and timechart | Splunk
How to color chart bar and highlight the threshold - Splunk Community
Solved: Add trendline to timechart splunk - Splunk Community

Creating Charts - Splunk Observability Workshops

Quick Guide to Outlier Detection in Splunk - Discovered Intelligence
Solved: Trellis layout for Line Chart in Dashboard Studio - Splunk ...
Splunk Stacked Bar Chart

Types Of Dashboards In Splunk - Design Talk

Prevent Outages | Splunk

Splunk IT Service Intelligence | Splunk

Working with Detectors · Splunk Observability Cloud Workshops

Splunk Line Chart Multiple Lines 2026 - Multiplication Chart Printable

Splunk Outlier Example at Carlos Huguley blog
Solved: Display only overlay values in a bar chart Splunk ... - Splunk ...
Splunk Stacked Bar Chart

Awesome ways you can use the Splunk App for Nextcloud - Nextcloud

Advanced Network Traffic Analysis with Splunk and Isovalent | Splunk

Visualising Network Patterns with Splunk and Graphistry | Splunk

The All New Performance Insights for Splunk | Splunk

Chasing a Hidden Gem: Graph Analytics with Splunk’s Machine Learning ...

Chart Detectors · Splunk Observability Cloud Workshops

The All New Performance Insights for Splunk | Splunk

A guide to the Power of Splunk Visualizations - Kinney Group
How we can create a line chart with the area betwe... - Splunk Community

Splunk 6.6 New Features - Part IV - Trellis Layout Visualization ...

Charts in the Splunk Metrics Workspace - Splunk Documentation
chart - Splunk Documentation
Chart Overlay - Splunk Community

The All New Performance Insights for Splunk | Splunk

Solved: Column chart with Multiple chart overlay series ? - Splunk ...

Predict Your Incident Tickets With Splunk MLTK | TekStream Solutions

Creating and Using New Custom Visualizations in Splunk 6.4 | Function1
How to create a barchart with multiple metrics (in... - Splunk Community

Splunk Timechart Command Tutorial - Master SPL Time Series ...

Suchbefehle > „stats“, „chart“ und „timechart“ | Splunk
Network Graph · splunk/splunk-3D-graph-network-topology-viz · GitHub

How to Compare Specific Time Values in Splunk Dashboards Part 2

Splunk Stacked Bar Chart

Types Of Charts In Splunk at Mitchell Trigg blog
How we can create a line chart with the area betwe... - Splunk Community

Creating Charts - Splunk Observability Workshops

Dashboard Studio: What's New in Splunk Enterprise 10.0 and 9.4 | Splunk
How to create a chart to show count of events by h... - Splunk Community
Splunk Stacked Bar Chart

Breaking Through the Threshold: Leveling up ITSI Adaptive Thresholding ...
Thresholds Significado at Cynthia Connor blog

Splunk: How-to Create Dashboards and Alerts | Medium

Create an overlay chart - Tpoint Tech

Breaking Through the Threshold: Leveling up ITSI Adaptive Thresholding ...

Breaking Through the Threshold: Leveling up ITSI Adaptive Thresholding ...
![[splunk] Visualizations](https://velog.velcdn.com/images/woococo/post/9720aad9-5b0e-4663-bf71-82d31069a59d/image.png)
[splunk] Visualizations

Create an overlay chart - Tpoint Tech

There is no upper limit on the maximum effect that can be detected in ...
Every Chart Contains Elements That Can Be Formatted
![[splunk] Visualizations](https://velog.velcdn.com/images/woococo/post/c5818b85-d5ab-403b-b6aa-31d5de3fc173/image.png)
[splunk] Visualizations